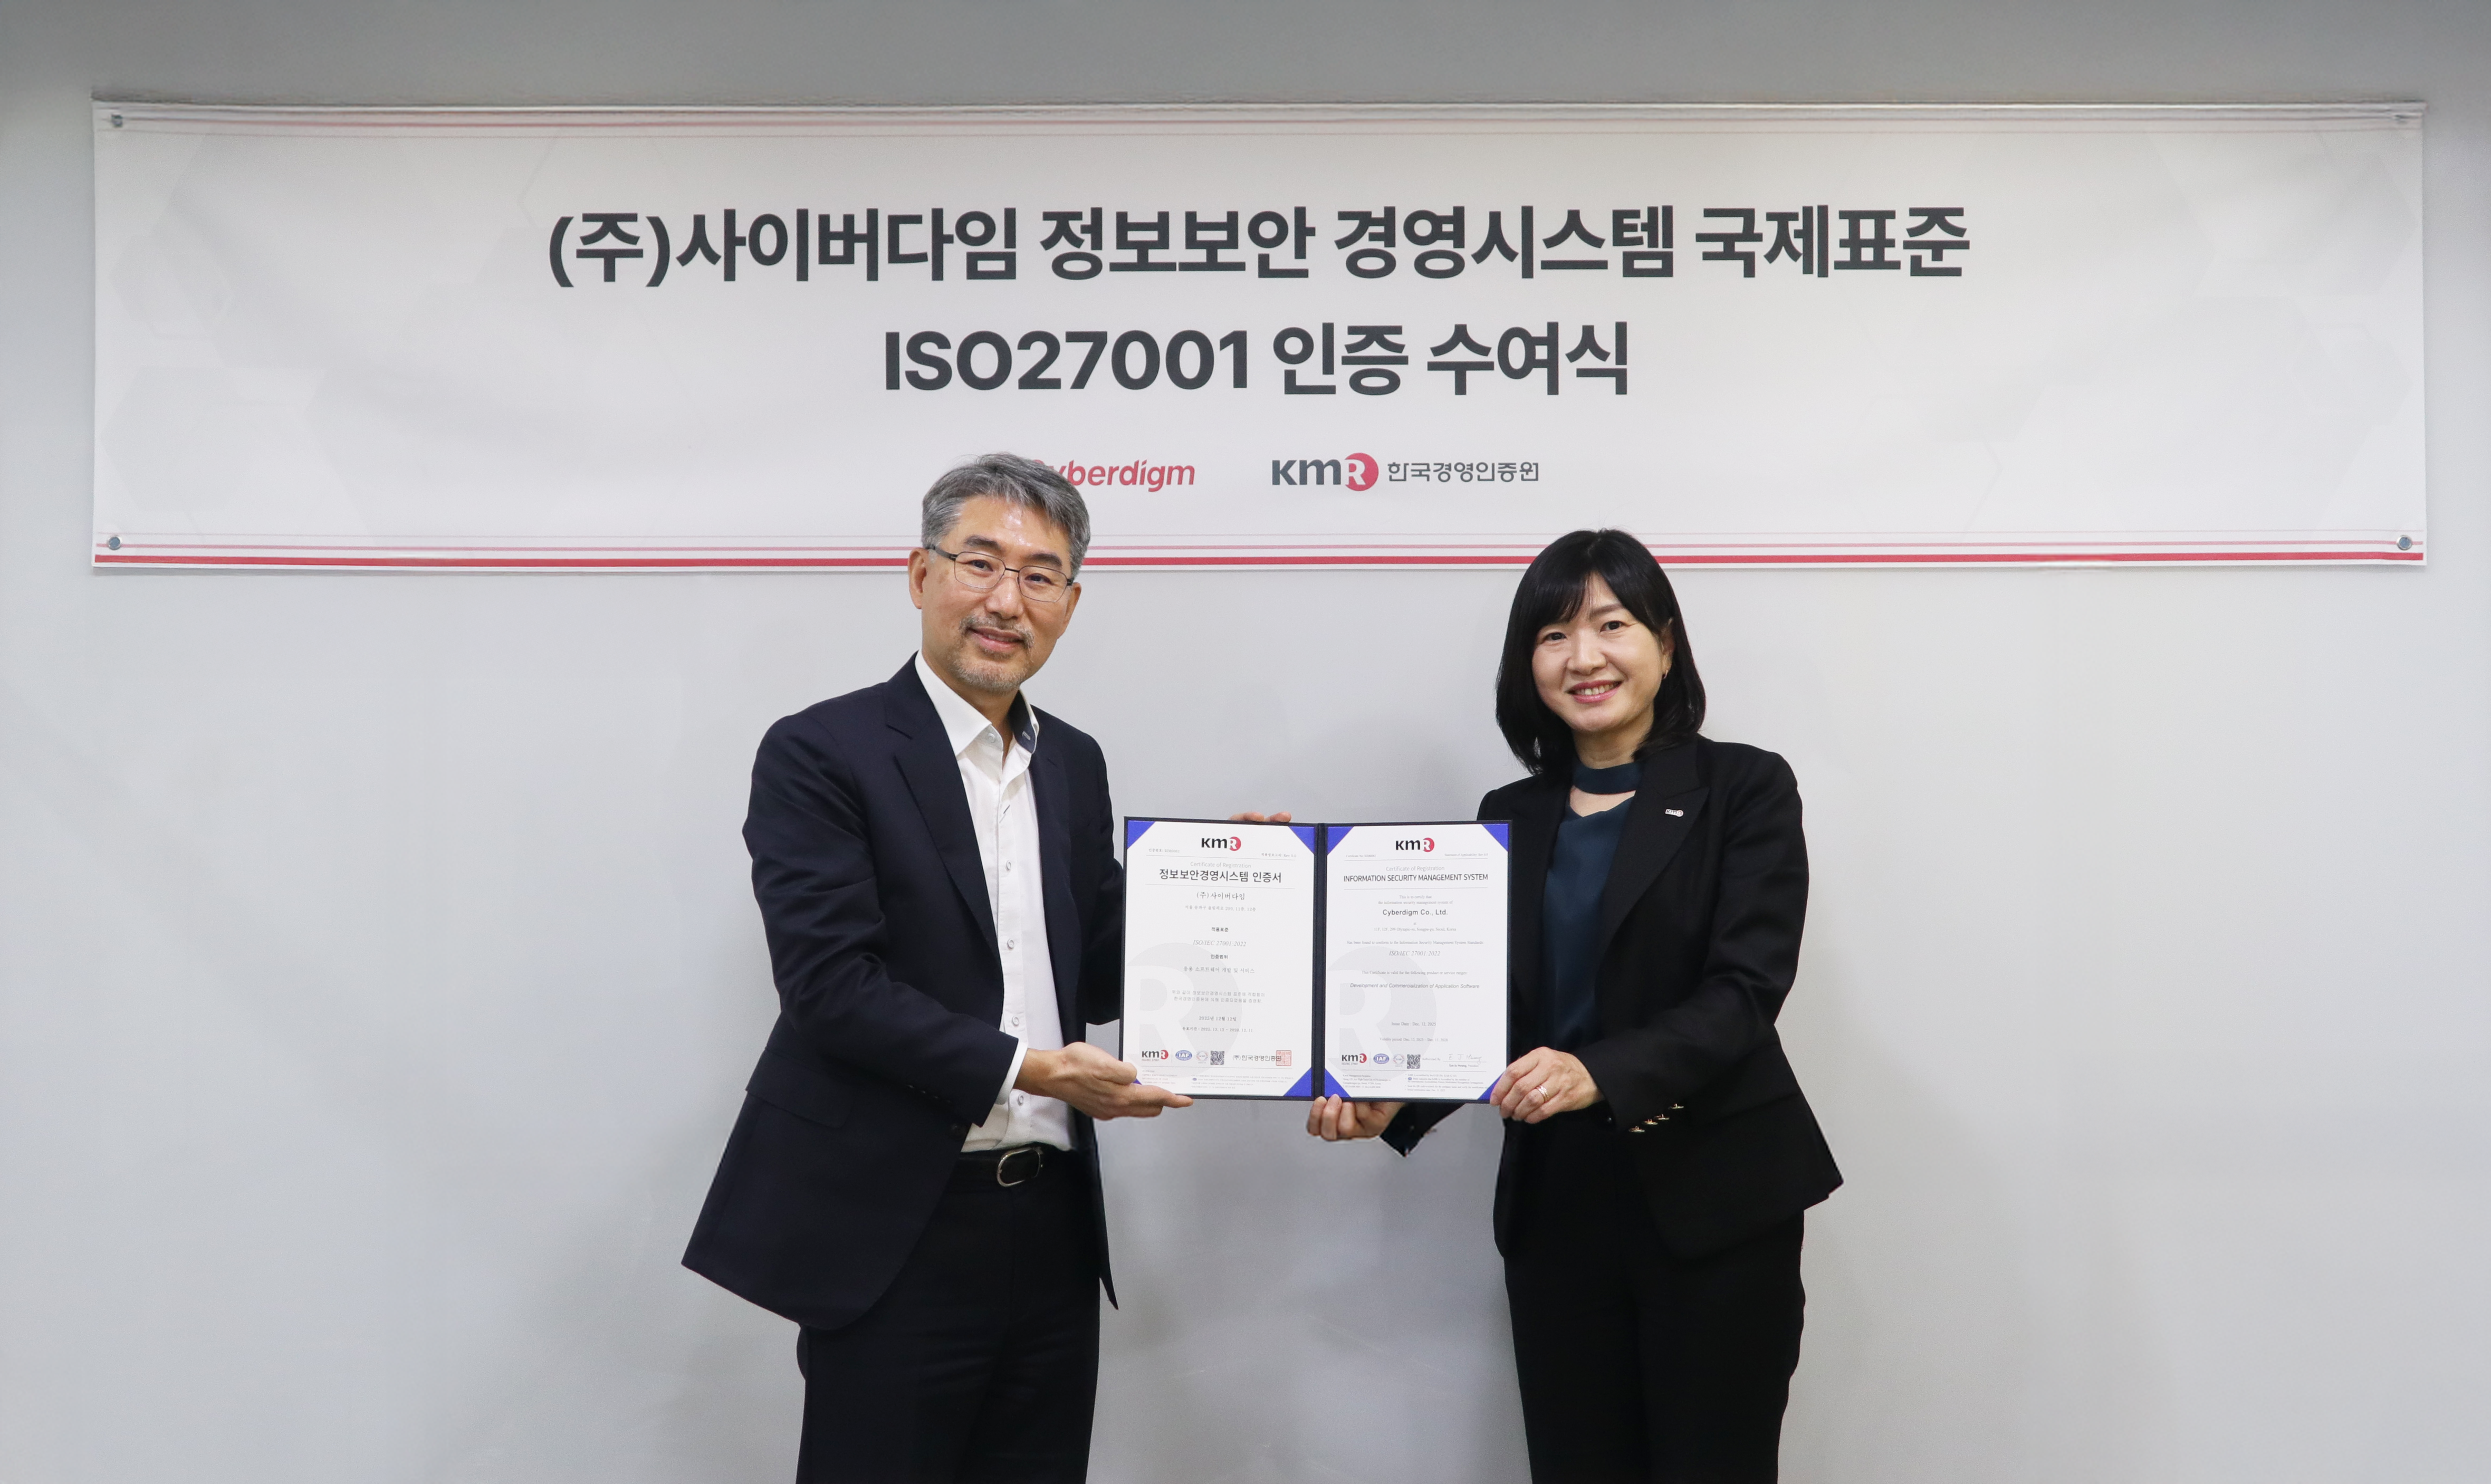
Cyberdigm (CEO Kyeong-Chae Kim), a leading specialist in Document Centralization Solutions and data security, announced that the company obtained ISO/IEC 27001 certification, an international standard for information security, from the Korea Management Registrar (KMR). An official certification ceremony was held on January 14, 2026.
ISO/IEC 27001 is an international standard for Information Security Management Systems (ISMS), jointly established by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC). This certification is awarded only after a comprehensive evaluation of 93 control items across organizational, human, physical, and technical domains to ensure the systematic protection of a company's information assets.
The certification audit covered Cyberdigm's entire range of application software development and services. The company was recognized for establishing an information security framework that aligns with global standards across all areas including ▲Information security policy and organizational operation ▲Security management during development and operational stages ▲Access control and authority management ▲Incident response and risk management
Since establishment, Cyberdigm has been continuously advancing technologies to safely manage and protect unstructured corporate data. The company focuses on structurally controlling information leaks and internal security risks that may arise throughout the entire document lifecycle, including storage, sharing, collaboration, and history management.
By utilizing its own solution, Cyberdigm has maintained rigorous information security practices to implement constant internal access controls and leak prevention systems. This practical operational experience and robust management framework served as the foundation for achieving the ISO/IEC 27001 certification. With this achievement, Cyberdigm plans to further reinforce employee security awareness and continuously upgrade its organizational information security level to remain aligned with international standards.
"This ISO/IEC 27001 certification is a formal external validation of our commitment to making information security a core value throughout our software development and service operations," stated Kyeong-Chae Kim, CEO.
He further commented, "As a provider of No. 1 Document Centralization Solution, we will continue to enhance our security frameworks and internal management standards to protect our clients' document assets and unstructured data, providing a secure environment where customers can operate with absolute trust and relief." Meanwhile, Cyberdigm plans to leverage this certification to strengthen the credibility of its Document Centralization Solutions and data security offerings, specifically targeting industries with high security requirements, such as finance, the public sector, and manufacturing.
Cyberdigm aquires Industry-First ISO/IEC 27001 Certification, Setting a New Global Standard for Information Security Management Systems

Cyberdigm (CEO Kyeong-Chae Kim), a leading specialist in Document Centralization Solutions and data security, announced that the company obtained ISO/IEC 27001 certification, an international standard for information security, from the Korea Management Registrar (KMR). An official certification ceremony was held on January 14, 2026.
ISO/IEC 27001 is an international standard for Information Security Management Systems (ISMS), jointly established by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC). This certification is awarded only after a comprehensive evaluation of 93 control items across organizational, human, physical, and technical domains to ensure the systematic protection of a company's information assets.
The certification audit covered Cyberdigm's entire range of application software development and services. The company was recognized for establishing an information security framework that aligns with global standards across all areas including ▲Information security policy and organizational operation ▲Security management during development and operational stages ▲Access control and authority management ▲Incident response and risk management
Since establishment, Cyberdigm has been continuously advancing technologies to safely manage and protect unstructured corporate data. The company focuses on structurally controlling information leaks and internal security risks that may arise throughout the entire document lifecycle, including storage, sharing, collaboration, and history management.
By utilizing its own solution, Cyberdigm has maintained rigorous information security practices to implement constant internal access controls and leak prevention systems. This practical operational experience and robust management framework served as the foundation for achieving the ISO/IEC 27001 certification. With this achievement, Cyberdigm plans to further reinforce employee security awareness and continuously upgrade its organizational information security level to remain aligned with international standards.
"This ISO/IEC 27001 certification is a formal external validation of our commitment to making information security a core value throughout our software development and service operations," stated Kyeong-Chae Kim, CEO.
He further commented, "As a provider of No. 1 Document Centralization Solution, we will continue to enhance our security frameworks and internal management standards to protect our clients' document assets and unstructured data, providing a secure environment where customers can operate with absolute trust and relief." Meanwhile, Cyberdigm plans to leverage this certification to strengthen the credibility of its Document Centralization Solutions and data security offerings, specifically targeting industries with high security requirements, such as finance, the public sector, and manufacturing.
Cyberdigm aquires Industry-First ISO/IEC 27001 Certification, Setting a New Global Standard for Information Security Management Systems