2025 was a challenging year for data security in South Korea. A telecommunications provider suffered a USIM-related data breach affecting 23 million users in April, followed by data breach from credit card company affecting nearly three million customers in August. Regulators identified weak internal controls as a key factor behind these incidents.
In response, the Korean government announced a comprehensive cybersecurity strategy. One of the key changes is the expansion of mandatory information security disclosure, which will apply to all listed companies in Korea as of 2027.
What Is Information Security Disclosure?
Information security disclosure requires companies to share information about their related investments, dedicated personnel, and certifications. Introduced in 2016 and made mandatory for selected organizations in 2022, the system helps investors and customers understand whether a company has the capability to protect its information assets
In 2025, 773 organizations submitted information security disclosures, including 666 companies subject to mandatory reporting. Their combined investment in information security reached KRW 2.42 trillion.
What are the expected changes in 2027?
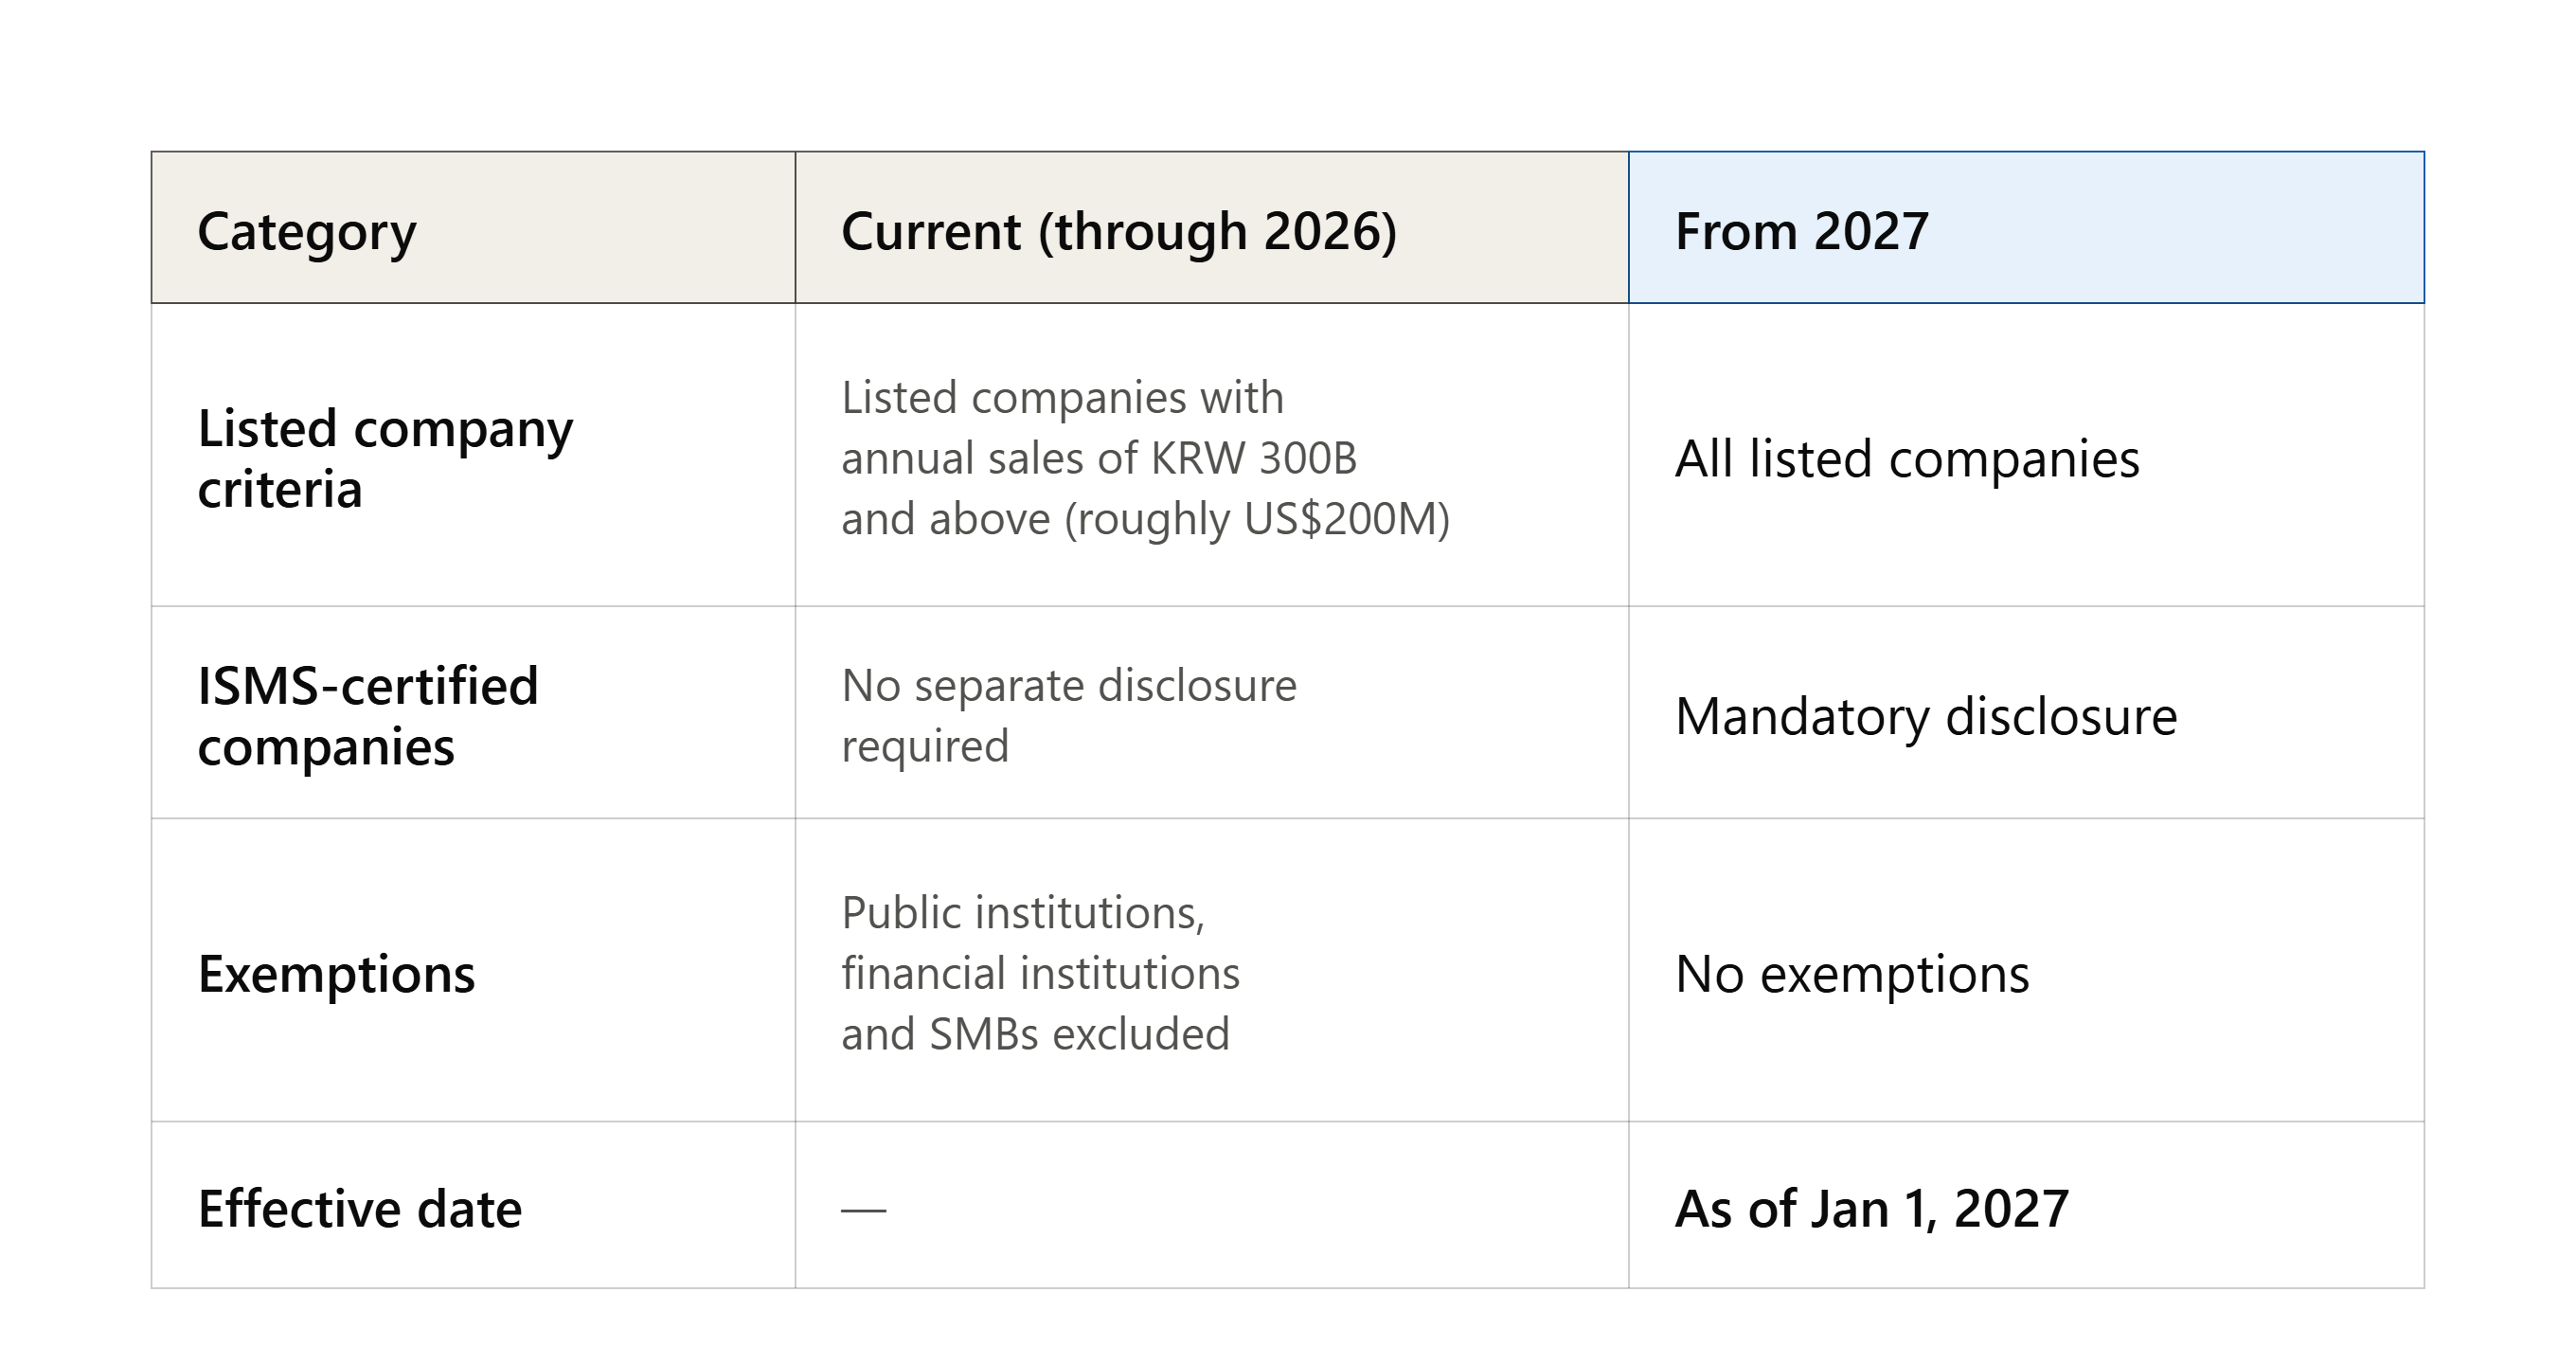
What are Disclosure requirements?
Companies will need to report:
- Information security investments
- Dedicated security personnel
- Security certifications and assessment status
However, information security is not a matter of investment size. Key question is whether those investments lead to effective security controls. Can a company track down access histories of critical information? Can they provide clear records of access and changes? These audit records are becoming essential for compliance and security management.
What Should Companies Prepare in advance
Most critical information is stored in documents including contracts, design files, proposals, and R&D materials. However, such documents are often scattered across individual PCs, shared folders, and email systems. Without proper control, companies may struggle to verify who accessed or modified important information.
DCS (Document Centralization Solution) enables organizations to securely manage documents while automatic recording of access, edits and transfer histories.
Ultimately, information security disclosure must align with proper security control and capability to provide necessary facts. As explained above, DCS provides a basis for information security disclosure.
Time to Prepare before it’s too late
With less than 6 months left in 2026, companies should start building access records before new compliance kicks in. Information security disclosure is becoming a key requirement for all listed companies in Korea. Cyberdigm is here to help organizations prepare for such requirements through secure document management solutions.
Sources
1. Mandatory Information Security Disclosure Expanded to All KOSPI and KOSDAQ Companies
2. ESG Economy, “Mandatory Information Security Disclosure to Apply to All Listed Companies from 2027
3. Security News, “All Listed Companies Required to Disclose Information Security Status from 2027
4. JoongAng News Media, “MSIT Releases Analysis Report on Corporate Information Security Investments and Personnel Disclosure in 2025
5. Biz Hankook, “Korean Companies Invest KRW 2.42 Trillion in Information Security
6. Digital Inclusion News, “Will 2025 Be Remembered as the Year of Data Breaches?
7. Kyunghyang Shinmun, “KT and Lotte Card Data Breaches: A Preventable Incident?
8. NordVPN, “Overview of Data Breaches in South Korea in 2025
#InformationSecurityDisclosure #MandatoryDisclosure #InformationSecurityIndustryAct #ListedCompanies #ISMS #DocumentCentralization #AuditLogs #EnterpriseSecurity #DataSecurity #Cyberdigm


2025 was a challenging year for data security in South Korea. A telecommunications provider suffered a USIM-related data breach affecting 23 million users in April, followed by data breach from credit card company affecting nearly three million customers in August. Regulators identified weak internal controls as a key factor behind these incidents.
In response, the Korean government announced a comprehensive cybersecurity strategy. One of the key changes is the expansion of mandatory information security disclosure, which will apply to all listed companies in Korea as of 2027.
Information security disclosure requires companies to share information about their related investments, dedicated personnel, and certifications. Introduced in 2016 and made mandatory for selected organizations in 2022, the system helps investors and customers understand whether a company has the capability to protect its information assets
In 2025, 773 organizations submitted information security disclosures, including 666 companies subject to mandatory reporting. Their combined investment in information security reached KRW 2.42 trillion.
Companies will need to report:
However, information security is not a matter of investment size. Key question is whether those investments lead to effective security controls. Can a company track down access histories of critical information? Can they provide clear records of access and changes? These audit records are becoming essential for compliance and security management.
Most critical information is stored in documents including contracts, design files, proposals, and R&D materials. However, such documents are often scattered across individual PCs, shared folders, and email systems. Without proper control, companies may struggle to verify who accessed or modified important information.
DCS (Document Centralization Solution) enables organizations to securely manage documents while automatic recording of access, edits and transfer histories.
Ultimately, information security disclosure must align with proper security control and capability to provide necessary facts. As explained above, DCS provides a basis for information security disclosure.
With less than 6 months left in 2026, companies should start building access records before new compliance kicks in. Information security disclosure is becoming a key requirement for all listed companies in Korea. Cyberdigm is here to help organizations prepare for such requirements through secure document management solutions.
Sources
1. Mandatory Information Security Disclosure Expanded to All KOSPI and KOSDAQ Companies
2. ESG Economy, “Mandatory Information Security Disclosure to Apply to All Listed Companies from 2027
3. Security News, “All Listed Companies Required to Disclose Information Security Status from 2027
4. JoongAng News Media, “MSIT Releases Analysis Report on Corporate Information Security Investments and Personnel Disclosure in 2025
5. Biz Hankook, “Korean Companies Invest KRW 2.42 Trillion in Information Security
6. Digital Inclusion News, “Will 2025 Be Remembered as the Year of Data Breaches?
7. Kyunghyang Shinmun, “KT and Lotte Card Data Breaches: A Preventable Incident?
8. NordVPN, “Overview of Data Breaches in South Korea in 2025
#InformationSecurityDisclosure #MandatoryDisclosure #InformationSecurityIndustryAct #ListedCompanies #ISMS #DocumentCentralization #AuditLogs #EnterpriseSecurity #DataSecurity #Cyberdigm